
SysAidIT Com Explained: Enterprise ITSM Platform Guide
What looks like a simple login domain usually turns out to be a governance question. SysAidIT com matters less as a marketing page and more as a tenant, access, and ownership signal, which is exactly why procurement teams should treat it as an enterprise control point instead of a generic web address.
The practical issue is not whether SysAid exists. It does. The core issue is what this specific environment is, who administers it, and how it maps to the licensed product, the tenant model, and the security boundaries your team will live with after go-live.
What SysAidIT Com Actually Is
SysAidIT com is best understood as a tenant-style environment, not a public product brochure. In practice, it often resolves to a Service Space page or customer-specific workspace rather than a broad marketing, pricing, or support portal, which is why buyers can get misled when they search the domain expecting a normal vendor site.
That distinction matters because enterprise ITSM buyers need to know whether they're looking at a shared brand asset or a controlled customer instance. If a domain behaves like a tenant entry point, the questions change fast. Who owns the environment, how is access provisioned, and what data-segregation model sits underneath it?
Why buyers misread the domain
The confusion usually comes from assuming every vendor URL works like a public homepage. SysAidIT com doesn't behave that way, so the buyer experience feels incomplete if you're expecting clear product positioning, support routing, or transparent tenant details.
A better question is whether the environment is customer-specific and how it is governed. That's where procurement, security, and service owners all need to align.
Practical rule: if a vendor domain behaves like a workspace, treat it as an operational asset, not a brochure.
The governance angle is why this domain keeps surfacing in buyer research. SysAid's own educational content stresses that organizations should be careful about who gets administrator access and which ITSM processes need to be live first, which fits the idea that tenant control matters as much as feature selection. For a procurement team, that means the domain isn't just a URL, it's part of the control surface.
For teams building a discovery path, the most useful internal reference is SysAid ITSM procurement context, because the commercial conversation should start with tenant fit, not with generic product adjectives.
Core ITSM Capabilities for Enterprise Teams
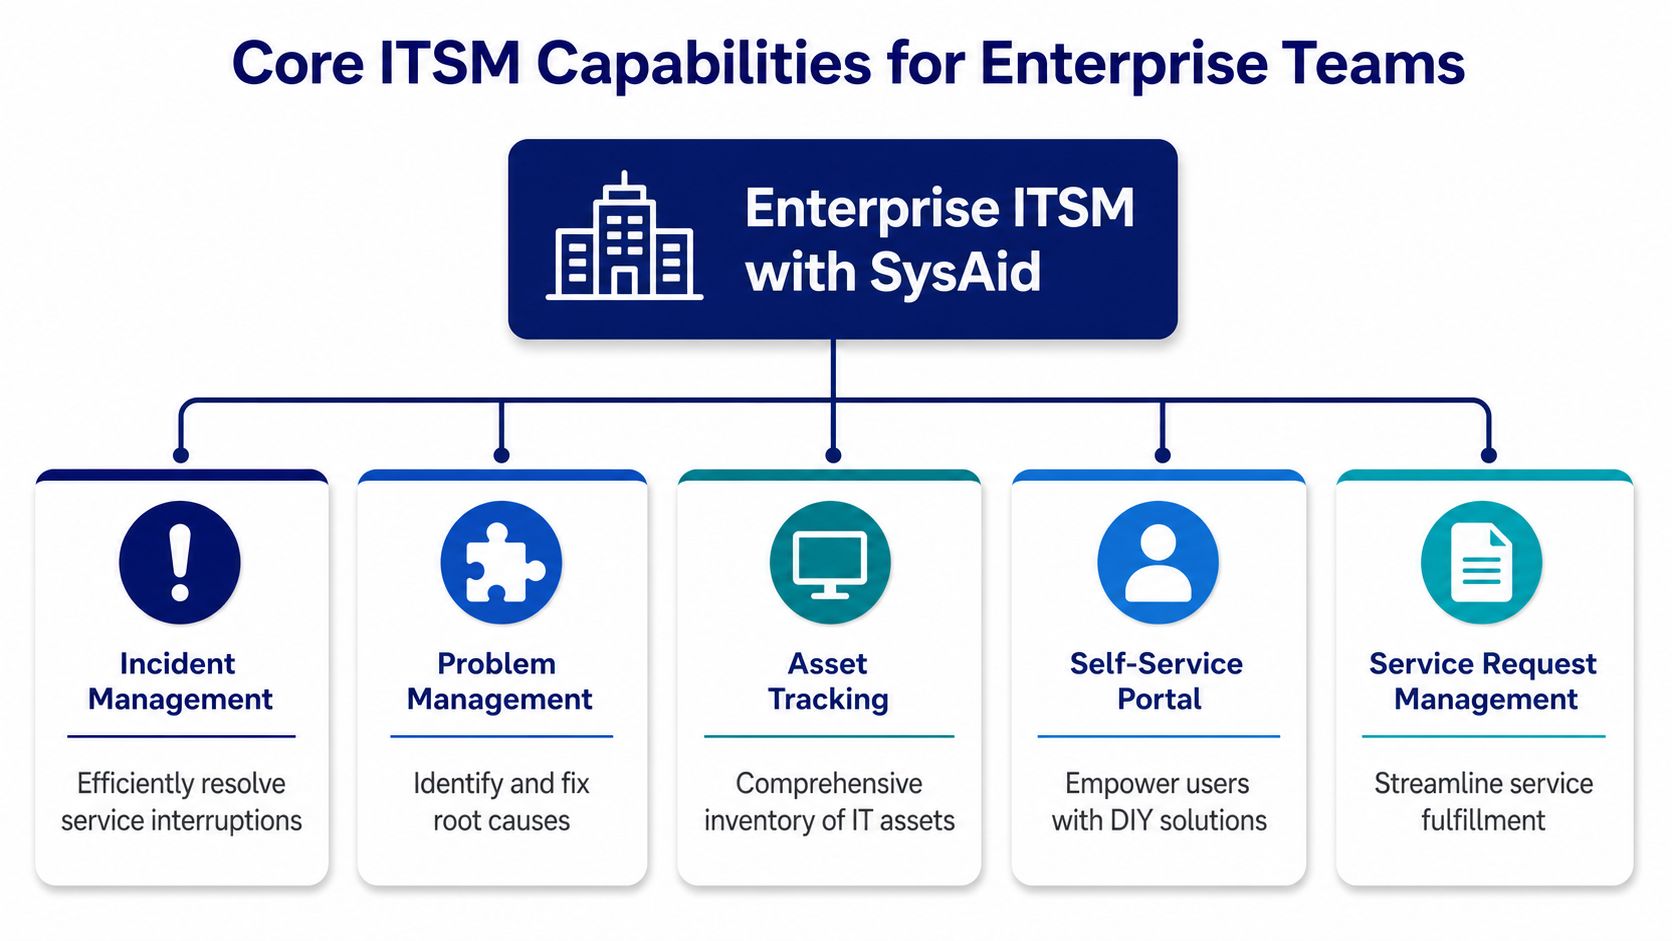
SysAid remains relevant as it encompasses the typical enterprise service desk backbone, including incident handling, problem management, asset visibility, self-service, and request fulfillment. The ultimate test is whether these capabilities reduce operational friction or merely add another platform to administer.
Where it tends to help
In a mature IT shop, incident management matters most when the queue is noisy and the team needs structured triage. Problem management matters when recurring issues keep coming back and someone has to own root cause, not just close tickets.
Asset tracking is valuable when the service desk, endpoint team, and procurement function all need the same inventory truth. Self-service and request management matter when the service desk is swamped with routine asks that end users can resolve or submit themselves.
A useful way to evaluate the platform is by workflow, not feature list:
Incident handling: useful when your team needs consistent classification and routing.
Problem management: useful when repeated failures are dragging down support quality.
Asset tracking: useful when CMDB-like visibility is part of governance.
Self-service portal: useful when users can be taught to search, request, and update on their own.
Service request management: useful when fulfillment needs standard steps and approval checks.
The strongest ITSM deployments are the ones where process owners define the workflow before the tool is turned loose on users.
That matters because ITSM tools often fail when teams buy the platform first and design the operating model later. If you want a pragmatic implementation view, SysAid ticket workflow guidance is a useful adjacent read for mapping features to actual service behavior.
Deployment Models and Infrastructure Requirements
How does SysAidIT Com fit into your environment without creating hidden infrastructure costs? The answer starts with how SysAid sizes deployments. The published installation guidance sizes on-premises environments by asset bands, and that is the more practical way to plan capacity because storage, hardware, and operating system constraints shift as the managed estate grows SysAid installation guide.
What the sizing bands mean in practice
The guidance ties the smallest band to 2.0 GHz CPUs and 2 GB RAM up to 500 assets, then moves to dual-core Xeon-class hardware at 500 to 2,000 assets, and then to quad-core Xeon-class hardware with 4 GB RAM above 2,000 assets SysAid installation guide. It also says environments over 2,000 assets require a 64-bit operating system and that expected database growth is 8 GB per 1,000 assets per year. Those points matter because the licensing conversation is only part of procurement. The infrastructure bill can rise as soon as the estate grows past the first band.
Asset Band | CPU Requirement | RAM | OS Architecture | Database Growth |
|---|---|---|---|---|
Up to 500 assets | 2.0 GHz CPUs | 2 GB | Not specified in the guide excerpt | 8 GB per 1,000 assets per year |
500 to 2,000 assets | Dual-core Xeon-class hardware | Not specified in the guide excerpt | Not specified in the guide excerpt | 8 GB per 1,000 assets per year |
Above 2,000 assets | Quad-core Xeon-class hardware | 4 GB | 64-bit OS required | 8 GB per 1,000 assets per year |
That table helps infrastructure and procurement teams see where the spend changes first. A growing estate pushes storage planning into the same conversation as processor sizing, and that is usually where unbudgeted work shows up.
The install checks that catch teams out
SysAid's technical presentation says .NET Framework 2.0 SP2 or above is required for network discovery SysAid technical presentation. The same material says the platform can use MS SQL Server, MySQL, or Oracle, but Oracle is not supported in version 21.4 and later, and if you bring your own MS SQL Server, the collation must be Latin1_General_CI_AS.
Those checks create familiar rollout risk. Discovery can fail if a prerequisite runtime is missing. Database behavior can drift if collation was never validated with the target environment. Upgrade planning gets harder if an older database choice is still in place, because the platform support line has already moved on.
SysAid on-premise planning notes is the right procurement companion when the deployment conversation shifts from feature fit to tenant structure, hosting responsibility, and what the implementation team needs on day one.
Integration Readiness and API Access Controls
SysAid's API access model is stricter than many procurement teams expect. The API overview states that access requires a SysAid account with Spaces infrastructure, SysAid administrator permissions, and SysAid user credentials SysAid API overview. That is not a single login path. It is a three-part control model that has to line up before integration work can start.
Why that matters for implementation teams
Tenant design can block an API rollout before the first test call is made. If the implementation team does not have admin rights, automation work stalls quickly. If credentials are not provisioned correctly in the platform, nothing else moves forward.
BI Analytics follows the same governance pattern. SysAid's documentation lists SysAid Service Desk, BI Analytics Access permission, and an email address defined in SysAid as prerequisites SysAid BI Analytics docs. The same documentation also says browser access to the Qlik-hosted dashboard requires third-party cookies allowed and the pop-up blocker disabled SysAid BI Analytics docs.
That matters in real deployments because access is not controlled only through licensing or role assignment. Browser settings can still break reporting for end users, so adoption teams need to test the actual user environment before they promise that analytics will work out of the box.
The least-privilege path
SysAid also gives administrators a more granular route for analytics access. An administrator can go to Tools > User Management > Administrators, open the relevant admin record, and enable “Access BI Analytics” on the Permissions tab, or grant access to a group SysAid BI Analytics docs. That split is useful because analytics access does not have to mirror full service-desk access.
For integration buyers, the practical checklist stays narrow:
Confirm the infrastructure model before any API work starts.
Validate admin permissions for the implementation team.
Check browser settings if analytics is part of the rollout.
Separate analytics access from broader admin access wherever possible.
API scope also needs to be tied back to the product's broader integration surface. SysAid integrations overview is the right reference if procurement wants to map access controls, integration effort, and vendor fit in one place.
Streamlining Procurement Through Stackingo
SysAid-style evaluations often get bogged down in fragmented quotes, side conversations, and vendor-specific packaging. That wastes time because buyers end up comparing proposals that weren't structured the same way in the first place.
Stackingo approaches that problem as a commercial front door for enterprise software licensing, including ITSM categories. It helps standardize the RFQ motion, compare offers more cleanly, and keep the buying team focused on requirements rather than on vendor-by-vendor negotiation noise. That is especially useful when the product decision depends on tenant fit, access controls, and infrastructure checks, because those details need to be captured consistently across quotes.
SysAid software procurement context is where many buyers should start if they want the commercial and operational questions in one place. It's a better fit than trying to piece together licensing logic from disconnected vendor conversations.
What structured buying changes
A structured buying process gives procurement and IT a shared record of what was asked for, what was priced, and what was included. That reduces back-and-forth and makes it easier to spot missing terms, mismatched support assumptions, or unclear scope.
Practical rule: the more a platform depends on permissions, infrastructure, and tenant design, the more important it is to centralize the commercial comparison.
That's where Stackingo fits naturally for enterprise buyers. It doesn't replace technical validation, but it does make the buying motion cleaner, which matters when you're comparing ITSM options under real time pressure.
Adoption Challenges and Real-World Fit
The hardest part of ITSM deployment is rarely installation. It's adoption. If users don't trust the portal, understand the workflows, or see quick value, self-service stays low and the service desk keeps absorbing routine work.
That's why the best-fit question matters. A full-featured ITSM platform can make sense for a mature IT organization with defined processes and enough internal ownership to maintain them. A smaller team may feel the process overhead faster, especially if ticketing discipline, admin coverage, and user training are still immature.
Not every team needs a broad platform on day one. Some need a simpler ticketing motion first, then move into deeper ITSM once the operating model is ready.
SysAid's own value-oriented content points toward self-service, triage, updates, and automation as the upside, but the buyer still has to do the work of teaching people to use those functions. If your rollout plan doesn't include communication, manager buy-in, and repeated user guidance, the platform can end up underused.
The honest test is this. Can the organization support the admin load, or is it trying to buy process maturity instead of building it?
Frequently Asked Questions About SysAidIT Com
Is SysAidIT com a public product site?Usually no. It behaves more like a tenant or Service Space environment than a broad public explainer. That's why buyers should verify ownership and access model before treating it as a standard vendor portal.
Who should evaluate the tenant or environment?Procurement, security, and the ITSM owner should all review it together. The key questions are admin control, access provisioning, and whether the environment maps to the licensed instance you expect.
Can SysAid integrations be assumed to work out of the box?No. The API model depends on infrastructure type, admin permissions, and valid credentials. Analytics access also depends on browser settings and separate permissions.
What does Stackingo add to the buying process?Stackingo gives enterprise buyers a structured way to compare licensing options through one commercial front. That helps when the evaluation depends on vendor scope, commercial terms, and implementation fit.
If you're comparing SysAid against other ITSM options, Stackingo can help you centralize the RFQ and keep the licensing process clear from the start. Visit Stackingo to compare options, capture requirements in one place, and move the procurement conversation forward with less friction.